
Penetration testing services
See every threat. Prevent every risk to business continuity. Automated scans catch typos, not attack paths. Our penetration testing consultants chain small flaws into real breach scenarios. We're ISO 27001 certified and test both complex enterprise platforms and startup solutions under NDA.
Industry leaders we work with


How can penetration testing protect your business?
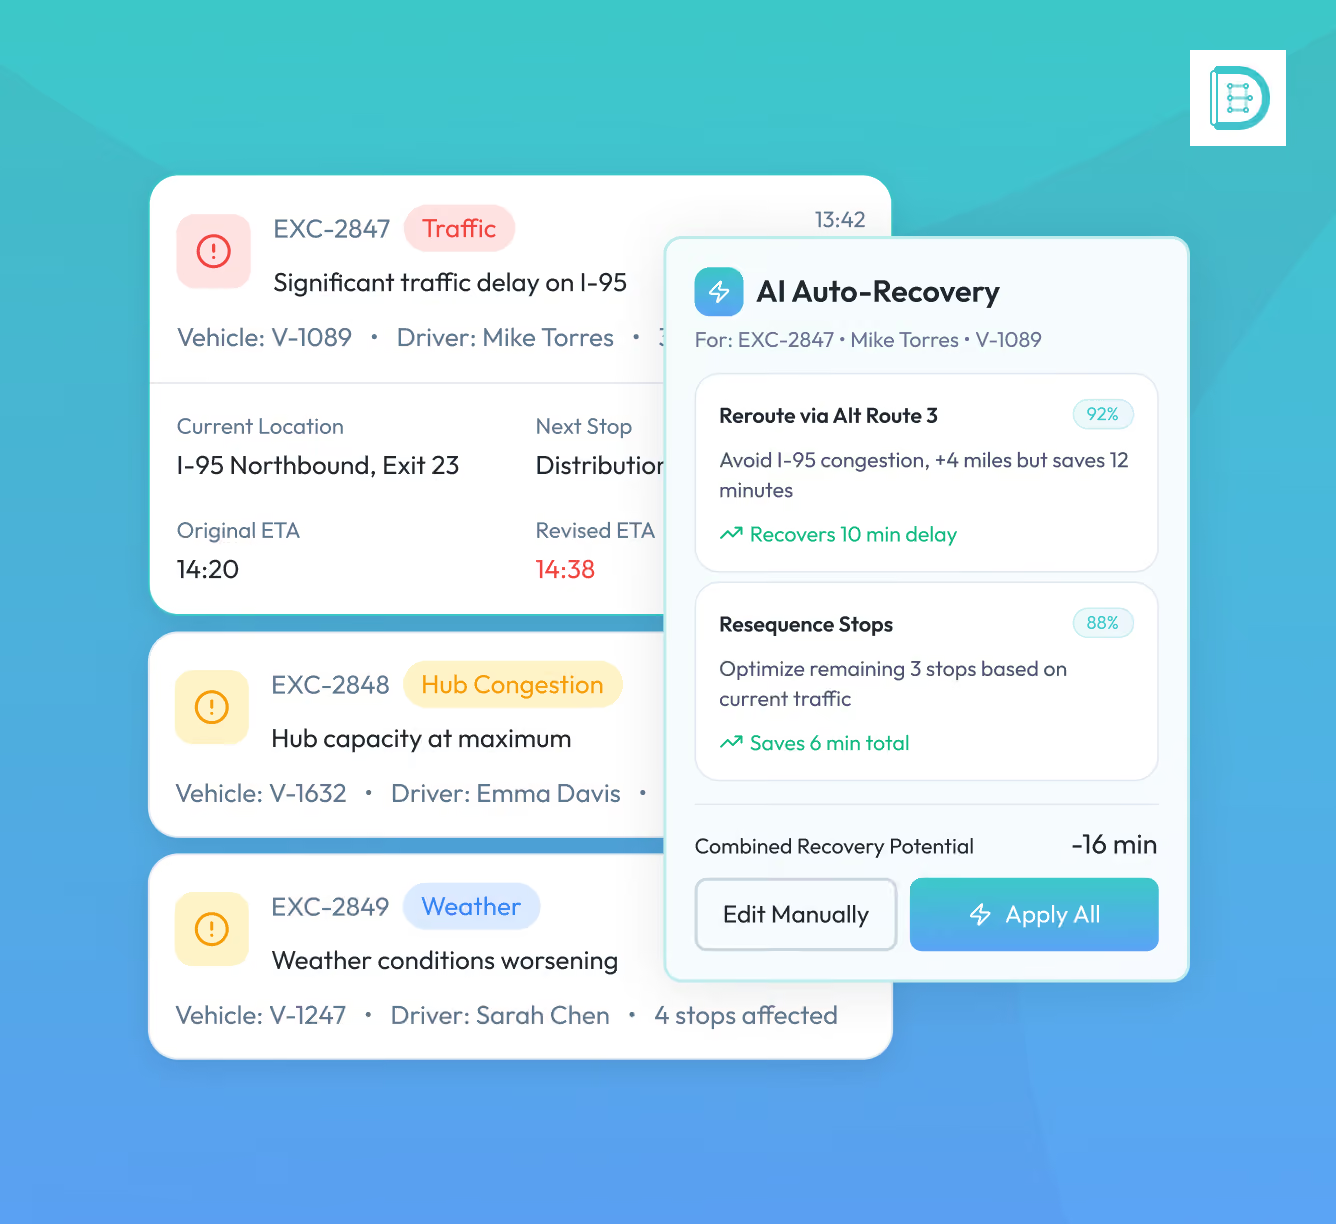
Our six-step pentesting process
We start by defining exactly what's in play, not guessing at boundaries mid-test. That means confirming target systems, testing windows, and rules of engagement upfront. A website penetration testing project needs different scoping than an internal network sweep. You get a signed-off scope before a single tool runs.
Deliverable: scope document, rules of engagement, testing schedule.
Attackers gather intelligence fast, and so do we. Our team maps your public footprint, open ports, subdomains, and exposed services. For AWS penetration testing services, for instance, that means enumerating S3 buckets, IAM roles, and misconfigured security groups before touching anything live. This phase builds the map everything else runs on.
Deliverable: asset inventory, attack surface map.
Automated scans flag the obvious; our engineers chase what scanners miss. We combine tooling with manual review across every layer in scope. Our vulnerability and penetration testing services blend both approaches deliberately, since scans alone leave logic flaws untouched. You get a ranked list, not a raw dump of alerts.
Deliverable: vulnerability findings log, initial risk ratings.
Finding a flaw isn't the same as proving it matters. We chain weaknesses together the way a real attacker would, carefully and under control. For API penetration testing services at this stage, we test broken auth, injection points, and rate-limit bypasses directly against live endpoints. Every exploit attempt stays scoped, logged, and reversible.
Deliverable: proof-of-concept exploits, exploitation log.
A finding nobody understands doesn't get fixed. We write reports your engineers and your auditors can both use. Each issue gets severity, business impact, and a clear reproduction path. No jargon dump, no forty-page filler nobody reads twice.
Deliverable: full technical report, executive summary.
Testing without a fix is just a list of open doors. We work alongside your team while they patch, then retest every closed item. This final pass confirms the fix holds, not just that a ticket got marked done. You walk away with verified, working defenses, not a hope they'll work.
Deliverable: retest report, closure confirmation, compliance-ready documentation.
Which security testing methodologies do we use?
Our core tech stack
Network Analysis
Nmap
Wireshark
Vulnerability Assessment & Scanning
Nessus
Nikto
OWASP ZAP
Web & API Penetration Testing
Burp Suite
SQLmap
Postman
Exploitation & Red Teaming
Metasploit
Cobalt Strike
BloodHound
Security Operations & Monitoring
Amazon GuardDuty
OS, Platforms & Environments
Kali Linux
Docker
Penetration testing vs. vulnerability scanning vs. security audit
Vulnerability scanning
Security audit
Penetration testing
What it does
Automated scan for known CVEs and misconfigurations
Reviews public exposure, headers, certs, and leaked data
Manually exploits real weaknesses to prove impact
Human involvement
None. Fully automated
Automated collection, human-reviewed findings
Hands-on exploitation by certified testers
Depth
Surface-level, broad coverage
Broad coverage with business context
Narrow scope, deep and adversarial
Output
Raw list of flagged issues
Executive and technical reports with priorities
Proof-of-concept exploits and a remediation path
Speed
Minutes
Minutes to hours
Days to weeks
Best for
Continuous, low-cost monitoring
Ongoing visibility into your attack surface
Proving what an attacker could actually do
Six reasons to trust our penetration testing services

Twenty years inside one demanding vertical
Booking engines, payment forms, and supplier integrations don't forgive sloppy security work. We've built and secured travel, logistics, and mobility platforms for almost two decades. Our mobile application penetration testing services draw on apps we've shipped ourselves, not just audited from outside.

We test what we've built, not just what we're told
Reading documentation only gets a tester so far. Our engineers have built the exact systems they now test: booking flows, marketplaces, and fleet platforms. That production background shapes how we run application penetration testing services, since we know where shortcuts hide.

Engineers who stay, context that compounds
Median engineering tenure at COAX runs 6.5 years, well above industry norms. The tester who ran your last engagement still knows your architecture. Our internal penetration testing services benefit most from that continuity, since lateral-movement risk depends on institutional memory.

Certified, audited, and NDA'd every time
We hold ISO 9001 and ISO 27001 certification company-wide, not as a marketing badge. Every engagement starts under NDA, before we touch a single credential. That discipline applies to a one-week scan and a six-week engagement alike.

Built for complex, connected stacks
Modern platforms rarely run on one clean system. They connect payment gateways, telematics feeds, and third-party APIs into one surface. Our web penetration testing services account for that complexity, since we've built the middleware connecting these systems ourselves.

Reports two audiences can actually use
A finding nobody understands doesn't get fixed. We deliver executive summaries for leadership and full technical evidence for engineers. Both come from one engagement, so nobody's translating findings into a second format later.
Trusted by our clients
Dan Brooks

President, Krytter
View showcase

Bohdan Zabawskyj
Co-founder and CPO at Fortay.ai
Neil Winkworth

ex-CTPO, Location Live
View showcase

Joseph Heenan

CEO, Proteineer
View showcase
Mykola Bronitskyy

Co-founder, GrandBus
View showcase

Other services
FAQ
Pricing depends on scope, not headcount. A single external network test can run far cheaper than a full application review with exploitation. Most first engagements land in the low-to-mid five figures, scaled by attack surface. We scope before quoting, so founders see cost tied to actual risk, not a flat rate pulled from a price list.
App store reviews check for obvious policy violations, not exploitable flaws. This testing goes deeper, examining API calls behind the interface, local data storage, and session handling on the device itself. We've caught insecure token storage that passed every store review without issue. Passing Apple or Google's checklist confirms baseline compliance, not real security against a determined, motivated attacker.
Yes, external testing targets what's already internet-facing, so it rarely touches production stability directly. We schedule intensive phases like exploitation during low-traffic windows and keep a rollback plan ready regardless. Downtime risk comes from live database changes, not simple probing. Founders worried about uptime should flag critical release dates during scoping, before testing windows are set.
Not necessarily. We can start from a simulated compromised laptop, a guest network, or actual VPN credentials, depending on what threat you're modeling. Remote and hybrid teams usually need the VPN scenario tested, since that's the real entry point attackers target now. The access model gets picked with you during scoping, matched to how your team actually works day-to-day.
We stop and notify you immediately, before continuing any planned testing. Every engagement includes an emergency contact clause for exactly this scenario. It's rare, but not unheard of, especially in unpatched cloud environments. Testing pauses until your team confirms the incident is contained, then resumes under a revised scope. Founders should never treat this clause as boilerplate; it matters.
SOC 2 questionnaires confirm that policies exist; they don't prove your code holds up under a real attack. This kind of testing checks actual endpoints, auth flows, and input handling live, not paperwork. Auditors accept both, but only one shows evidence of real resilience. We've seen companies pass SOC 2 with vulnerabilities a first-day pentest would catch immediately. Compliance and security aren't the same thing.
Usually, yes, since most diligence checklists ask for evidence of testing against your live application. Term sheets increasingly include a security review clause, and scrambling after signing looks worse than planning. Startups that book testing early get a clean report to hand over, not a rushed scramble under deadline pressure. We've supported founders through exactly that timeline crunch before.
What we’ll do next?
1
Contact you within 24 hours
2
Clarify your expectations, business objectives, and project requirements
3
Develop and accept a proposal
4
After that, we can start our partnership